EU AI Act Info

AI Compliance OS

The software tool that helps your company stay compliant.

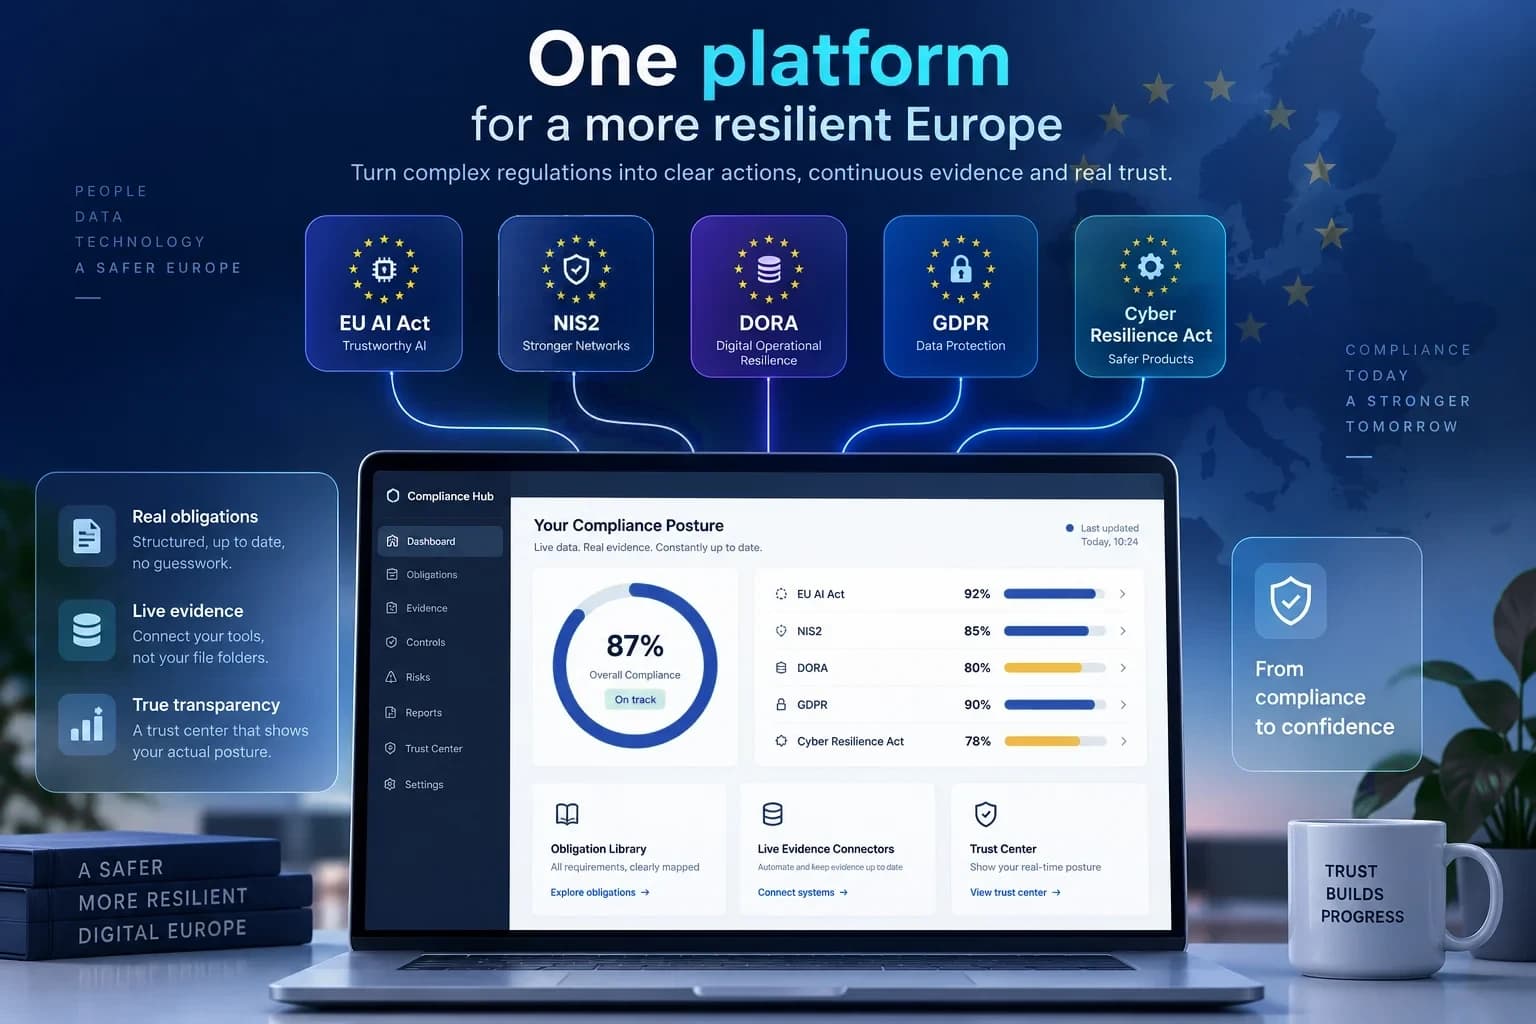
Built for the EU AI Act, the NIS2 directive, DORA and the Cyber Resilience Act.

Artwork: the EU AI Act, NIS2, DORA, GDPR and the Cyber Resilience Act feeding one compliance dashboard on a laptop
0
Real obligations, each cited to primary law
0
EU regulations covered
0
AI-driven connections built
EU
Hosted infrastructure, by default

See it in motion

One minute through the real product, paced so you can read every screen: the score, the clocks, the graph, the audit pack.

How it works

How we scan your business

No consultant on site and no hundred-page questionnaire. You give the software four kinds of information, and it checks every legal requirement that applies to you against them.

  1. 01

    Your company profile

    About five minutes

    Where you are based, your sector and size, and whether you use or build AI. From these answers the software works out which EU laws apply to you.

    • Country and sector
    • Number of employees
    • AI use, financial services, connected products
  2. 02

    The readiness check

    Twenty yes-or-no questions

    Short questions drawn from the laws in scope. They give you a first picture of where to focus, before any evidence is in.

    • Would MFA stop someone with a stolen password?
    • Could you respond to an incident within 24 hours?
    • Have you restored from backup this year?
  3. 03

    Your tools, read-only

    Microsoft 365 and GitHub today

    You grant read-only access and the software checks your real settings — for example, whether every user and administrator signs in with multi-factor authentication. It never changes anything.

    • Microsoft 365 / Entra ID
    • GitHub
    • Google Workspace, Okta, AWS and Azure next
  4. 04

    Your documents and registers

    Upload or type in

    Upload your policies and link each one to the requirement it covers. Then add what no tool can see: people and training, suppliers and certificates, AI systems, assets and risks.

    • Policies and procedures
    • Supplier certificates and contracts
    • AI systems, assets, risks

The scan

Then it scans

  1. Every requirement gets a verdict — proven, partly proven, out of date or missing — with the evidence behind it.

  2. Where a record and the evidence disagree, you get a finding: an expired supplier certificate, an AI system with no risk level.

  3. Every gap becomes a task with a due date, and your compliance score rises as you close them.

Every requirement ends up as one of

  • Proven
  • Partly proven
  • Out of date
  • Missing

Your data

  • Stored in the EU (Frankfurt)
  • Connections are read-only
  • Visible only to your organisation
  • Nothing is public until you press Publish

Your private AI system does the work.

It runs on your own data, inside your own workspace, and nothing it reads ever leaves. Here is what it does, step by step.

  1. 01

    It connects

  2. 02

    It checks

  3. 03

    It scores

  4. 04

    It plans

An AI-driven connection to the tools you already use, GitHub and Microsoft 365 today. It only reads. It never changes anything, and it never interferes with your privacy.

Every check is saved as a piece of evidence with a source, a time and a tamper-proof seal. Nothing is ever overwritten, so an auditor can see what was true and when.

It works out exactly which requirements of each EU law apply to your company and gives you a personal compliance score. Every verdict shows its reasoning, so you can see why.

Then it turns every gap into a clear list with a timeline and a course of action. Your score, your trust center and your audit pack all read the same record.

GHM365MFA enforcedgithub · 99%verified 3 h agosealed · linked to the record beforeControlArt 21(2)(j)NIS2Trust center live

Inside the platform

Real screens from a demo organisation, not mock-ups. This is what the system builds for you, and what a compliance officer sees every day.

  • We build your trust centre

    The one the NIS2 directive expects, and the one your customers ask for when they check their own suppliers. Published from your dashboard, at the level of access you choose.

  • Your personal compliance score

    Our AI system works out exactly which requirements of each EU policy and law apply to your company, and scores you against them, with the reasoning shown rather than hidden.

  • A clear plan, with dates

    Then it turns every gap into a list: what to do, in what order, by when. Statutory deadlines are counted for you from the moment something happens.

euaiactinfo.com/t/demo-org
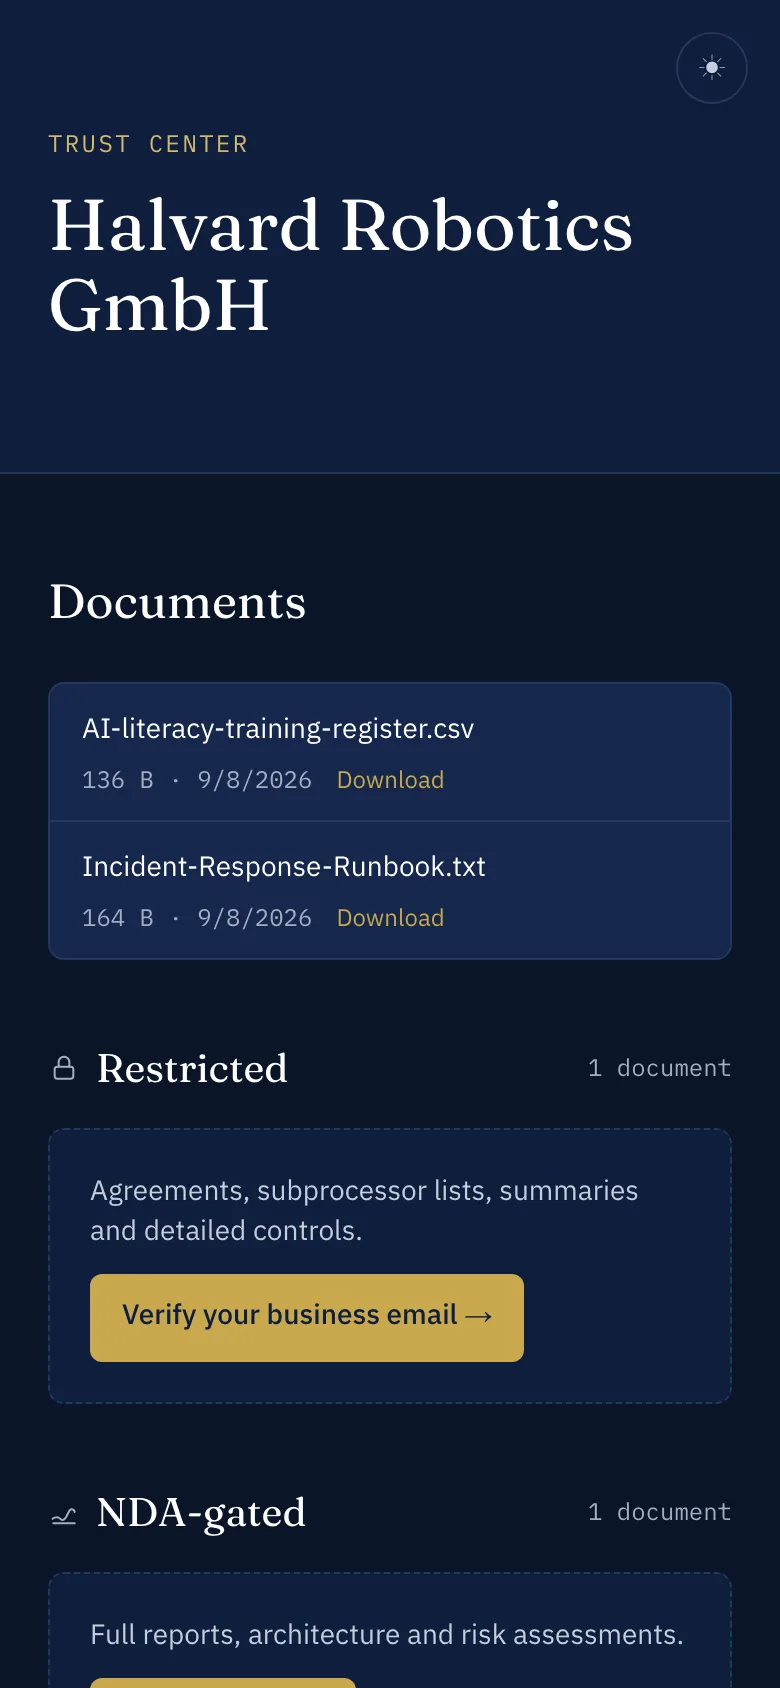
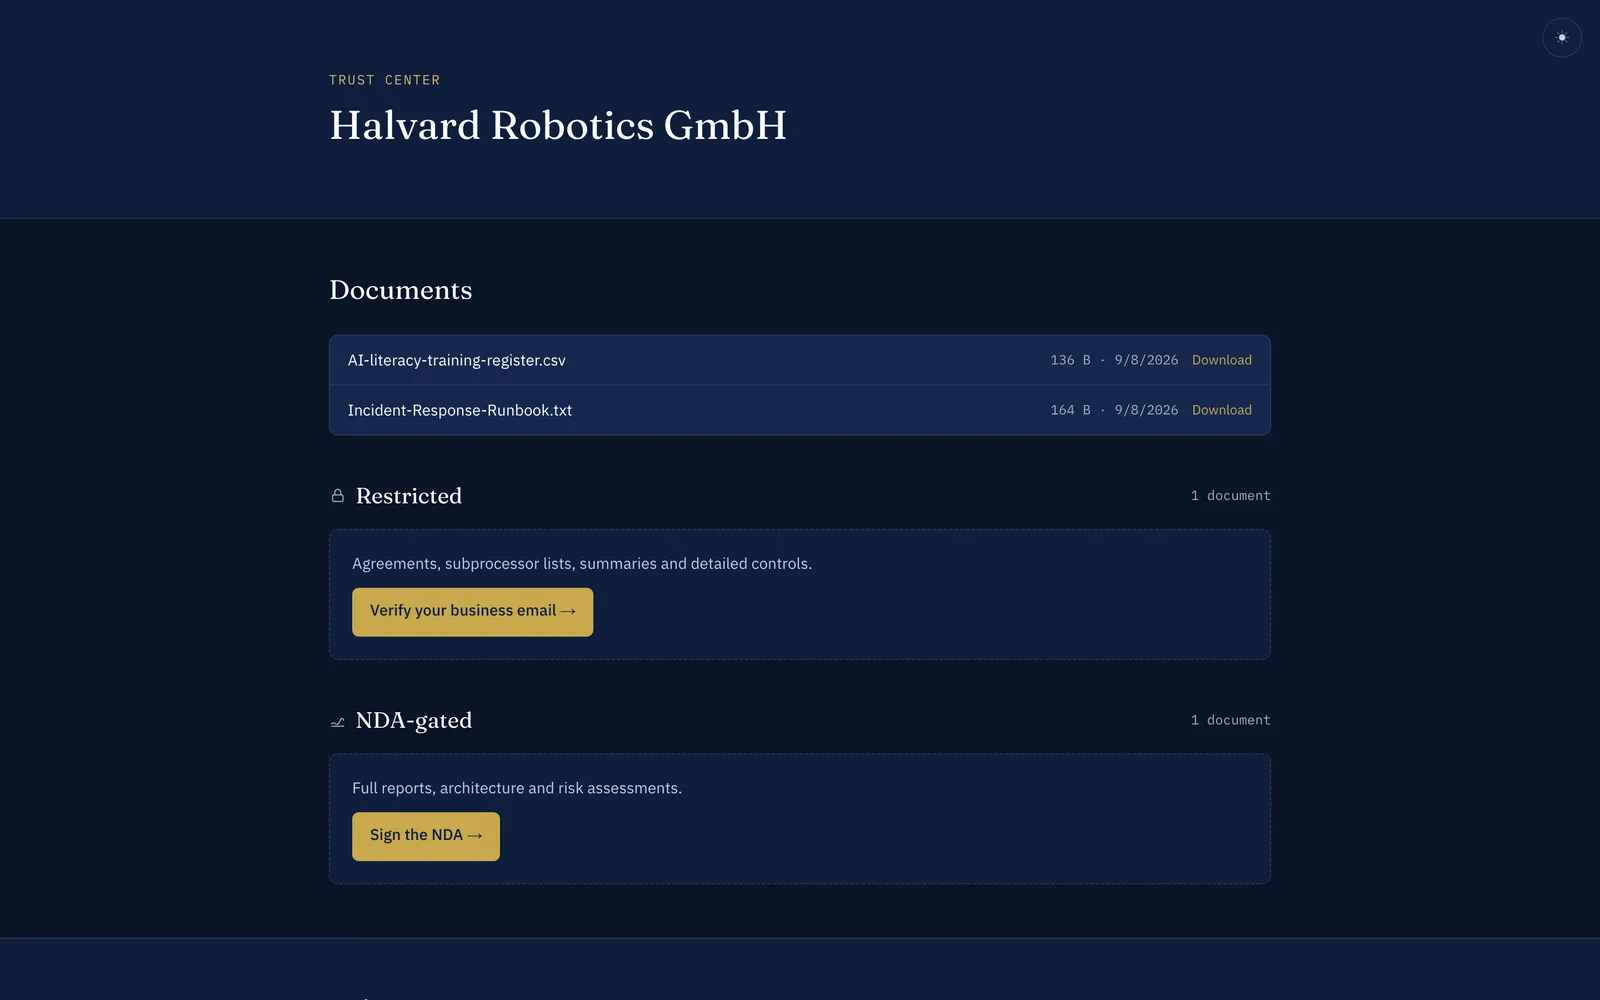
The public trust center page of a demo organisation, listing documents and published policies

Eight screens — use the arrows to see each one.

Screen 1 of 8

Your public trust center

A page where customers and auditors find your security documents themselves, instead of sending you the same questionnaire again.

  1. Public documents anyone can download
  2. Restricted documents unlocked with a verified business email
  3. Sensitive documents only after an NDA is signed

Which EU laws apply to you?

Four answers. The same rules the onboarding wizard runs, against the real obligation library.

Employees
AI

Choose a sector to see your scope.

The same rules run in the onboarding wizard. A starting point, not a legal determination.

Every module, one record

Sixteen modules reading the same evidence: four to prove it from the law, ten to run the organisation the regulations assume, two to publish what is true. Each one carries five marks showing which European laws it reads from — pick one below to see how far it reaches.

Reads from

Each card's five marks read left to right: NIS2 · GDPR · EU AI Act · CRA · DORA.

Built for the people who carry the duty

Three views of the same evidence. Each one is a real screen in the platform, not a persona on a slide.

  • COMPLIANCE SCORENIS2AI ACTGDPR

    Managing director

    Can we prove compliance right now?

    One compliance score, the open incidents with their statutory clocks, and every high risk on a single screen. Drill down when the board asks why.

    In the platform: Executive overview

  • Compliance officer

    What needs doing today

    Statutory clocks first, then overdue tasks, then every place a policy claims one thing and the evidence on file shows another.

    In the platform: Workspace

  • MFA enforcedgithub · 99%sealed · linked to the one beforeMFA enforcedmicrosoft365 · 97%sealed · linked to the one before2FA re-checkgithub · 99%sealed · linked to the one before

    IT and security lead

    Evidence without the questionnaire

    The AI-driven connection reads GitHub and Microsoft 365 and turns each check into sealed, dated evidence. The MFA question is answered by the system, not by email.

    In the platform: IT and security view

What your buyers see, tier by tier

Tap a tier. The same evidence, revealed to the right audience.

Gate

No gate. Indexed by search engines and AI assistants.

Buyers research you before they contact you.

4 of 12 items visible at this tier

  • Security overview
  • Compliance framework status
  • Certifications and badges
  • Data residency
  • Data processing agreementRestricted
  • Subprocessor listRestricted
  • Service-level agreementsRestricted
  • Penetration test summaryRestricted
  • Full penetration test reportNDA-gated
  • Architecture diagramsNDA-gated
  • Risk assessmentsNDA-gated
  • Sensitive policiesNDA-gated

Statutory clocks, live

incident detected 45 min before you opened this page

  • NIS2 · Early warning

    NIS2 Art 23(4)(a)

    Due
  • NIS2 · Incident notification

    NIS2 Art 23(4)(b)

    Due
  • NIS2 · Final report

    NIS2 Art 23(4)(d)

    Due
  • DORA · Initial notification

    DORA Art 19(4)(a); Del. Reg. (EU) 2025/301

    Due
  • DORA · Intermediate report

    DORA Art 19(4)(b)

    Due
  • DORA · Final report

    DORA Art 19(4)(c)

    Due
  • GDPR · Breach notification

    GDPR Art 33(1)

    Due

The same rules run on every incident you record. The platform counts the duty down; it is not the channel that discharges it.

Every verdict shows its chain

A real obligation, a real check. Rules decide; nothing here was written by a model.

  1. Regulation

    Directive (EU) 2022/2555 (NIS2)

    Source: regulations/text/NIS2.txt:1745

  2. Obligation

    NIS2-021-2j · Article 21(2)(j)

    Multi-factor authentication or continuous authentication

  3. Control

    MFA enforced for all users

    Direct evidence of Art 21(2)(j)

  4. Evidence

    github · 99% · today

    18/19 members (95%) have 2FA enabled; 0 of 2 owners lack 2FA

  5. Verdict

    SATISFIED

    Verified via github today at 99% confidence.

A real obligation library, not a checklist template

77 obligations across 6 regulations, each citing the exact regulation, article and source line it comes from, traceable to the official EUR-Lex text.

Explore the obligation library →
  • artificial intelligence5
  • Cyber Resilience Act2
  • digital operational resilience11
  • data protection3
  • cybersecurity8
  • NIS2 Art 21(2) technical requirements48

What's actually true about us

  • Your records are stored in the EU (Frankfurt) by default, not as a footnote.
  • Every regulatory citation traces back to the official legal text (EUR-Lex), not a marketing summary.
  • No invented logos, no fabricated customer counts, no stock people. The product-tour screenshots are real; the hero artwork is illustrative.
  • We're early. Sign up now and you're a design partner with direct input into the roadmap.

Estimate your time saved

A rough estimate, not a guarantee. It assumes a live trust center replaces about 75% of the time spent answering a security questionnaire from scratch.

~108 hours/year

Estimated from the assumption above. Adjust the numbers to match your own team.

Built for your sector

Each page runs the scope finder with a typical profile for that industry, so what you see is computed from the rules, not asserted.

Questions we get asked

Does this replace our ISMS or GRC tool?

No. Your management system stays the system of record for controls and risks. This is the evidence and proof layer: it decomposes the law into obligations, checks the evidence, and shows the result to buyers, auditors and the board without duplicating the ISMS.

Does the AI decide our compliance?

The AI system does the legwork: it connects to your systems, collects the evidence, works out which requirements apply to you, scores you and schedules what needs doing. Every verdict is decided by rules you can inspect, and every one shows its reasoning from the article of law to the evidence, so nothing is a black box. There is also an AI register for the AI tools your company uses.

Which regulations are covered?

The EU AI Act, NIS2 and Implementing Regulation 2024/2690, DORA and Delegated Regulation 2025/301, GDPR and the Cyber Resilience Act: 77 obligations, each cited to the official EUR-Lex text and source line.

Where is our data?

The database is PostgreSQL on Supabase in Frankfurt (eu-central-1), with each company's data kept strictly separate at the database level. Application compute runs on Vercel, currently in US East. The security page says exactly what is and is not in place.

What does it cost?

Nothing today. The platform is free for design partners while it is early, with every module included and no card. We give notice before any plan carries a price.

Can we see it without signing up?

Yes. The live demo signs you into a seeded organisation, read-only, with every module populated.

Is the scope finder legal advice?

No. It applies the directive's own size gate and sector lists and the onboarding wizard's rules, and it says it is a starting point. Scope determinations are yours and, where applicable, the competent authority's.

Publish your trust center in an afternoon, not a quarter.

No credit card, no sales call. Sign up, upload your evidence, publish.

Get started free →